
Technical Onboarding Center
Most cloud problems that hurt later are decided in the first few weeks. Who can sign in, who can grant access, where projects live and how networks connect are all easy to get wrong when the only goal is "get something running." The Technical Onboarding Center exists to make those early decisions deliberately, so an organization becomes productive on Google Cloud from day one without paying for shortcuts afterwards.
This post opens a series that walks through that foundation piece by piece. Here you get the map: what onboarding covers, how the work is staged, and which steps come in which order. The following posts zoom into each step.
Why onboarding deserves its own process
The objective is simple to state and hard to do well: establish strong cloud foundations quickly while keeping security, governance and scalability intact. Speed and safety usually pull in opposite directions. Teams that move fast skip the guardrails, and teams that build every guardrail first never ship.
The Technical Onboarding Center resolves that tension with three ingredients: automation, lean processes and a structured delivery model. Automation makes the foundation repeatable, so the tenth environment looks like the first. Lean processes keep the ceremony proportional to the risk. The delivery model brings identity, networking and security together, instead of letting each team configure its own corner in isolation.
The result is what the approach calls accelerated onboarding: a shorter time to value, secure foundations from the start, consistent deployments and a smoother experience for the customer.
The four onboarding stages
Before anyone touches the console, the work moves through four stages. Each one exists to remove a specific kind of surprise from the next.
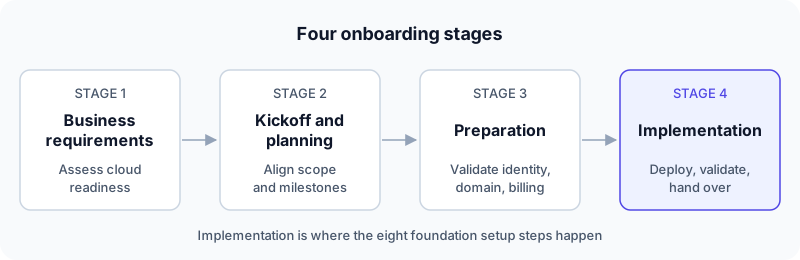 The four onboarding stages, from assessing readiness to handing over a working foundation
Business requirements comes first because you cannot design a foundation without knowing what it has to carry. The current environment, objectives, constraints and target architecture are reviewed to assess cloud readiness. The output is an honest picture of how prepared the organization is to move to Google Cloud.
Kickoff and planning turns that picture into a shared plan. Stakeholders are identified and aligned, and scope, milestones and deliverables are agreed on. This is where you discover that the network team and the security team had different timelines in mind, which is far cheaper to learn in a meeting than in production.
Preparation clears the path. Orientation sessions bring everyone up to speed, and prerequisites are validated: identity, domain and billing configurations are reviewed and any issues are fixed before deployment begins. Imagine discovering halfway through setup that nobody has access to the company's DNS records. Preparation is the stage that catches that early.
Implementation is where the foundation is actually deployed, using automation tools and the Google Cloud Console. Best-practice configurations are applied, the environment is validated, documentation is completed, and the setup is handed over to the migration or application teams who will build on it.
The eight foundation setup steps
Inside the implementation stage, the foundation is built in a fixed order. The order matters: each step depends on the ones before it, the same way you cannot assign roles to a group that does not exist yet.
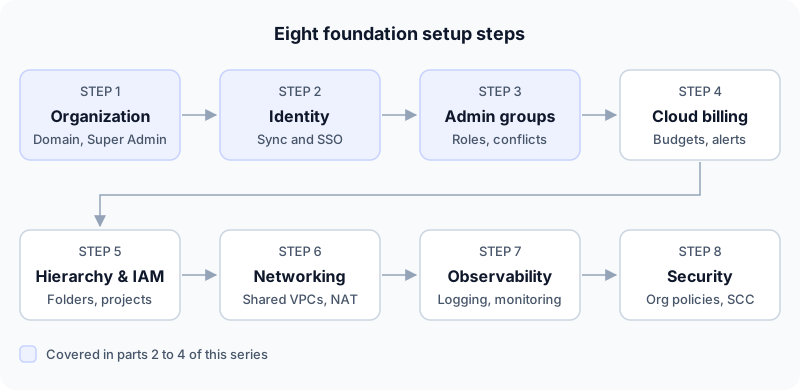 The eight foundation steps. The highlighted ones are covered in the next three posts
It starts with the organization: a Google Cloud organization is created, the customer domain is verified, and Super Admin accounts plus the recommended administrative user groups are configured. Next comes identity: Cloud Identity is set up, with synchronization when required, primary or secondary identity providers are integrated, and single sign-on is implemented if needed. Then admin groups and access: administrative groups are created and assigned recommended roles, users are mapped to the right groups, and conflicts with unmanaged accounts are identified and resolved.
With people and permissions in place, cloud billing is set up. Billing accounts are created and linked based on customer requirements, either online self-serve or invoiced billing, and budgets, billing alerts and billing export reports are configured. Then the resource hierarchy and IAM: an initial set of folders and projects is deployed, and Identity and Access Management permissions are applied using group-based access and least privilege.
Networking follows, with Shared VPCs configured per environment in a hub-and-spoke model, and firewall rules, NAT and hybrid connectivity implemented according to the network design and security requirements. Monitoring and logging are centralized with Cloud Monitoring and Cloud Logging, so metrics, events and logs from all projects can be used for observability and troubleshooting. Finally, security: recommended organization policies are enforced and Security Command Center is enabled, giving centralized visibility into the security posture.
Notice that identity sits at the very beginning. Every later step, from billing to networking, assumes you already know who your users are and how they are grouped. That is why the next three posts in this series focus entirely on identity and access.
Choosing your tooling
You have two broad ways to build this foundation, and the right choice depends on how often you expect to do it again.
| Approach | What it gives you | Good fit when |
|---|---|---|
| Console-based workflows | A guided enterprise foundation setup driven by a structured onboarding checklist | You are setting up one organization and want guidance at each step |
| Cloud Foundation Toolkit | Baseline implementations of Google Cloud best practices as infrastructure as code (Terraform, Deployment Manager, Kubernetes Resource Manager) | You need repeatable, reviewable, version-controlled foundations |
The console is the faster way to learn what each step does. Infrastructure as code is the better way to make sure the next environment matches the last one exactly, and to review foundation changes the same way you review application code.
Tip: Even if you start in the console, write down every decision you make. Those notes become the requirements for the infrastructure-as-code version later.
Wrapping up
Technical onboarding is about making the foundational decisions on purpose rather than by accident. Four stages (requirements, planning, preparation and implementation) make sure the work starts from a clear, agreed plan, and eight ordered foundation steps build the environment from identity outward to security. Get those right, and teams can spend their time building value on a foundation that already scales. The next post starts at the beginning of that chain: Cloud Identity and the Google Cloud organization.