
Hybrid Connectivity
Very few companies move to the cloud in one step. Databases stay on-premises while applications move, a data center contract runs for another two years, or part of the platform lives in another cloud provider. Hybrid connectivity is how you securely connect those environments to Google Cloud, and it underpins migrations, hybrid architectures and multi-cloud strategies alike.
In the previous post you built a custom mode VPC with your own IP ranges. This post connects that network to the outside world. Google Cloud offers two primary managed options, Cloud VPN and Cloud Interconnect, and the right choice depends on your latency, bandwidth and availability requirements.
Cloud VPN: encrypted tunnels over the internet
Cloud VPN is the fastest and simplest way to connect Google Cloud to an external environment. It builds IPsec tunnels over the public internet and encrypts traffic between your VPN gateway in Google Cloud and the peer gateway on the other side. Because it rides on the internet connection you already have, you can usually set it up in an afternoon rather than waiting on a physical circuit.
Cloud VPN supports high availability, static routing, and dynamic routing with BGP. It is the usual choice when low latency is not a strict requirement. There are two gateway types, and for anything new the decision is easy.
Classic VPN
Classic VPN uses a single interface with a single external IP address. It supports site-to-site connectivity, static routing and limited dynamic routing scenarios. The peer gateway must have a static external IPv4 address. Classic VPN provides a 99.9% service availability SLA and does not support IPv6.
It is generally used for legacy setups and is not recommended for new deployments. If you find one in an existing environment, plan to replace it rather than extend it.
HA VPN
HA VPN is the recommended option for new deployments. It uses two interfaces, each with its own external IPv4 address, and relies on dynamic routing with BGP. Each interface can carry multiple tunnels, and each tunnel provides up to roughly 1.5 to 3 Gbps. When you need more throughput, you add tunnels to raise the aggregate bandwidth. HA VPN provides a 99.99% service availability SLA.
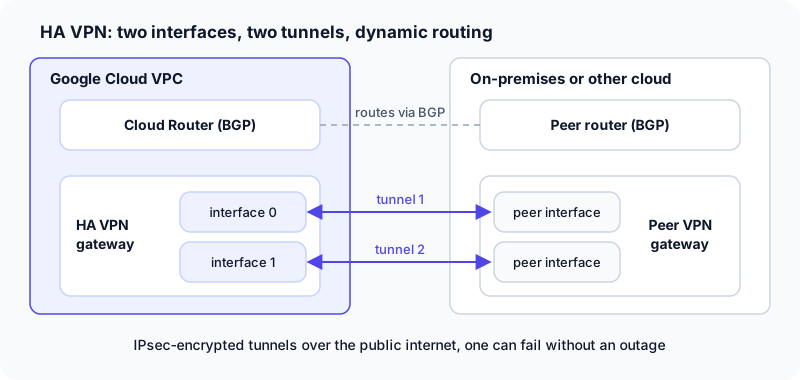 HA VPN: two interfaces and two tunnels, with routes exchanged over BGP
The reason for two interfaces is resilience. With traffic spread across tunnels on both interfaces, losing one tunnel does not take the connection down, and BGP updates the routes so traffic shifts to the healthy path without someone editing route tables at 3 a.m. That is what makes HA VPN suitable for production workloads that need reliable connectivity.
When Cloud VPN is enough
Cloud VPN is a good fit when you need connectivity quickly, your bandwidth needs are moderate, your latency requirements are flexible, and connecting over the public internet is acceptable. A typical example: a team migrating a few internal services that still call an on-premises database a few hundred times a minute. The traffic is modest and a few extra milliseconds do not matter, so HA VPN gets them connected now without any physical work.
Once you need low latency and high bandwidth, for example replicating large datasets continuously or serving latency-sensitive traffic across the boundary, Cloud Interconnect is the better option.
Cloud Interconnect: a private path into Google's network
Cloud Interconnect provides private, enterprise-grade connectivity directly into Google's network instead of over the public internet. It is designed for high-bandwidth, low-latency use cases, and it comes in two forms.
Dedicated Interconnect is a direct physical connection between your on-premises infrastructure and Google Cloud through a colocation facility. Links are 10 or 100 Gbps, giving high throughput and low latency. The price of that performance is responsibility: you need physical presence in a supported colocation facility, you manage your own routing equipment, and the service availability SLA ranges from 99.9% to 99.99% depending on how you build it. It suits large environments with consistent, high data transfer needs.
Partner Interconnect reaches Google Cloud through a supported service provider. The provider manages the physical connectivity, bandwidth options are flexible, and there are fewer technical prerequisites, with a 99.99% service availability SLA. It is the natural choice when direct colocation is not feasible or when you do not need full-size links, and it still gives you private access to Google Cloud.
Comparing the options
Put side by side, the four options line up along a spectrum from "fast to set up" to "maximum performance":
| Option | Path | Capacity and traits | Availability SLA |
|---|---|---|---|
| Classic VPN | IPsec over the internet, one interface | One external IP, no IPv6, legacy | 99.9% |
| HA VPN | IPsec over the internet, two interfaces | ~1.5–3 Gbps per tunnel, more with extra tunnels | 99.99% |
| Dedicated Interconnect | Direct physical link at a colocation facility | 10 or 100 Gbps links | 99.9% to 99.99% |
| Partner Interconnect | Through a service provider | Flexible | 99.99% |
A sensible way to decide is to start from your requirements, not the product list. If you need private, high-throughput, low-latency connectivity and already have equipment in a supported colocation facility, Dedicated Interconnect fits. If you want private connectivity without the colocation work, look at Partner Interconnect. If the internet is acceptable and you mainly need something reliable and quick, HA VPN is the default. Classic VPN only appears in that conversation when you are maintaining something that already exists.
Getting the VPN configuration right
Most VPN problems are not product problems. They are mismatches between the two ends. Before you declare a tunnel broken, check that both sides agree on the basics:
- Public IP addresses are configured correctly on both gateways.
- Routing configuration is consistent on both ends.
- Pre-shared keys match exactly.
- Firewall rules allow the VPN traffic.
Tip: Make these checks part of a written runbook and repeat them after any change on either side. A key rotated on-premises but not in Google Cloud looks exactly like an outage.
This is also where the IP planning from the previous post pays off. If your VPC ranges overlap with on-premises ranges, routing across the tunnel becomes painful no matter how well the tunnel itself is configured.
Wrapping up
Hybrid connectivity lets your Google Cloud environment work with everything that is not in it yet. Cloud VPN gives you encrypted tunnels over the internet, and HA VPN, with two interfaces, BGP and a 99.99% SLA, is the default for anything new. Cloud Interconnect gives you a private path into Google's network: Dedicated when you can bring your own equipment to a colocation facility and need 10 or 100 Gbps links, Partner when you want private connectivity through a provider. Match the option to your real latency, bandwidth and availability needs, keep both ends of a VPN configured consistently, and you will have connectivity you can build on. Once traffic is flowing, you need to see it, which is where logging and monitoring come in.