
Data Privacy in Practice
Every organization handles personal data, whether it is a customer database, an HR system, or the analytics on a website. Data privacy is about how that information is collected, used, stored, shared, and protected, and getting it wrong is expensive: regulatory exposure, reputational damage, security incidents, and a loss of trust that is hard to win back. Most of it comes down to a handful of habits you can build into everyday work.
What counts as personal data
Personal data is any information relating to an identified or identifiable living person. The word "identifiable" does a lot of work here. A name or an identification number points to someone directly, but location data or an online identifier such as a cookie can identify a person indirectly, especially when combined with other information. In a typical organization, personal data shows up in staff records such as HR data, in customer relationship data, and in reader or user data collected through websites and digital platforms.
Some personal data deserves extra protection. Special categories of personal data are types of information that may make an individual particularly vulnerable: physical or mental health, racial or ethnic origin, political opinions and political party membership, religious or philosophical beliefs, sex life, sexual orientation, trade union membership, genetic data, and biometric data. Because the risk is higher, stricter legal requirements apply. In many situations this data can only be processed when explicit consent has been obtained or another valid legal basis applies.
The distinction is not academic. Customer service notes about a complaint are personal data, while occupational health records are special category data. Salary details are personal data, while political affiliation is special category data. Knowing which bucket you are in tells you how careful you need to be, because higher sensitivity means higher compliance requirements.
The regulatory landscape
Obligations depend on geography, and global organizations have to align their controls across several regimes.
| Region | Key frameworks | What stands out |
|---|---|---|
| EU | GDPR | Principles-based, applies beyond EU borders |
| UK (ICO) | UK GDPR, Data Protection Act 2018, PECR | Accountability, documentation, marketing rules |
| UK (Ofcom) | Online safety and communications regulation | Children and digital platforms |
| US | CCPA/CPRA, FTC enforcement, HIPAA, COPPA | Fragmented, sector- and state-specific |
The General Data Protection Regulation applies across the EU and to organizations processing EU residents' data, including organizations outside the EU that offer goods or services to people in the EU or monitor their behavior. It is built on seven principles: lawfulness, fairness and transparency, purpose limitation, data minimization, accuracy, storage limitation, integrity and confidentiality, and accountability. Failing to comply can lead to reputational damage, regulatory enforcement, and significant financial penalties, with fines of up to £17.5 million or 4% of global turnover, whichever is higher.
In the UK, the Information Commissioner's Office (ICO) is the independent authority for data protection and privacy. It oversees the UK GDPR (the post-Brexit version of GDPR), the Data Protection Act 2018, and PECR, the Privacy and Electronic Communications Regulations. The ICO expects demonstrable accountability, strong governance and documentation, a clear lawful basis for processing, and compliance with specific rules for marketing communications such as cookies, email, and SMS.
Ofcom regulates UK communications services, including broadcasting, telecoms, and online safety. It is not a data protection regulator, but it matters where privacy meets media and digital platforms: protecting users, especially children, online safety obligations for platforms, and communications data in regulated services. If you work on content platforms, audience measurement, advertising technology, or children's services, Ofcom belongs on your radar.
The United States has no single federal privacy law equivalent to GDPR. Instead there is a combination of federal and state laws, such as the California Consumer Privacy Act (CCPA) and CPRA, Federal Trade Commission enforcement against unfair or deceptive practices, HIPAA for health data, and COPPA for children under 13. The result is fragmented and varies by state and industry, but common themes emerge: transparency through privacy notices, consumer rights such as access, deletion, and opt-out, disclosures about selling or sharing data, and sector-specific compliance.
Tip: Rather than a separate process per jurisdiction, apply the highest appropriate standard where you can. One baseline is easier to operate and explain.
Privacy across the data lifecycle
A consistent privacy framework covers privacy by design, transparency, individual rights, secure sharing, children's data, responsible marketing, retention and deletion, and lawful international transfers. The easiest way to make that concrete is to follow personal data through its life.
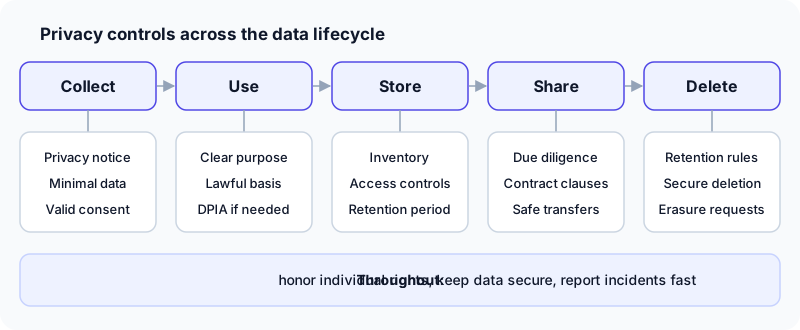 Each step in the data lifecycle has its own privacy controls
Before you collect: privacy by design
Privacy by design means making privacy an integral part of products, services, and processes from the beginning instead of bolting it on later. In practice, new projects or activities involving personal data should be reviewed early, so risks can be assessed and controls put in place while changes are still cheap.
For high-risk processing, that review takes the form of a data privacy impact assessment (DPIA), completed before the processing starts. Processing special categories of data, systematically evaluating or predicting personal aspects of people, and large-scale processing of personal data are all examples of high-risk work. Imagine a feature that scores millions of customers on their likely interests: that is both systematic evaluation and large scale, so a DPIA comes first.
Collect: be transparent
Transparency means people understand why their data is collected, how it is used, and what choices they have. This is normally done through a privacy notice, which should be available at the time data is collected, explain clearly how it will be used, and be accessible in context, including at online collection points. Notices should be reviewed whenever new initiatives or process changes are introduced, and where a change is significant or outside what people would reasonably expect, the updated notice may need to be actively communicated rather than quietly published.
Marketing deserves its own care. Under GDPR and the ICO, electronic marketing is governed by consent and PECR rules, while in the US opt-out frameworks such as the CCPA apply. Either way, good practice is the same: offer clear and specific marketing options at the point of collection, make it easy to withdraw consent or opt out, include an unsubscribe method in every marketing message, respect objections promptly, and keep records of consent and preferences.
Children's data is a higher-risk area that always calls for careful review. That can mean carrying out a privacy impact assessment before collecting it where appropriate, applying age thresholds that depend on the jurisdiction, obtaining parental or guardian consent where required, and using age-appropriate design with additional safeguards. Both the ICO and Ofcom emphasize special safeguards here, COPPA applies in the US, and editorial or public interest contexts involving minors need extra care.
Use and store: keep a record
Organizations are required to maintain an internal record of how personal data is used. This data processing inventory captures the name and details of the data controller, the purpose of processing, the categories of individuals and of personal data involved, the categories of recipients, any international transfers and their safeguards, retention periods, and the security measures in place. Keeping it accurate is a core part of accountability: it is your answer when anyone asks what you do with the data.
Share: trust, but verify
Personal data should only be shared with third parties when adequate safeguards are in place. Before sharing, make sure the sharing is fair, lawful, and secure, that the third party has appropriate security controls, that contracts include suitable data protection clauses, and that secure transfer methods are used. When you engage a new supplier, due diligence is how you confirm they can protect the data they will process.
International transfers need additional care. The transfer must be lawful, appropriate safeguards must be in place, local legal requirements must be considered, and privacy and security teams should be consulted where necessary. Common safeguards include Standard Contractual Clauses (SCCs), adequacy decisions, and transfer risk assessments. Cross-border data flows should never be treated as routine without checking the regulatory implications.
Requests for personal data from public authorities, regulators, or law enforcement are a special case. They should always be referred through the appropriate internal legal or privacy channels, never handled casually or without review.
Delete: don't keep it forever
Personal data should not be kept longer than necessary. Set a retention period for each category of data based on the purpose it was collected for, legal and regulatory requirements, and genuine business and record-keeping needs. When the data is no longer needed, delete it securely. Clear retention schedules reduce risk directly: data you no longer hold cannot be lost or misused.
Respecting individual rights
People have important rights over their personal data, and organizations must be ready to respond promptly. These include:
- Access to their personal data
- Correction of inaccurate data
- Deletion where appropriate, and objection to certain processing
- Complaints about how their data is handled
- Portability (GDPR and UK GDPR)
- Opt-out (US)
Requests to stop marketing must be respected whatever channel they arrive through: an unsubscribe link, a phone call, an email, or a letter.
The right to erasure, sometimes called the right to be forgotten, lets individuals request deletion in certain circumstances, for example when the data is no longer needed for its original purpose, when consent has been withdrawn, or when there is no longer a lawful basis for processing. These requests need careful assessment and a response within the required timeframe.
A subject access request (SAR) is a request from an individual to access the personal data held about them. It entitles them to confirmation that their data is being processed, a copy of it, and additional information about how it is used. Under GDPR and UK GDPR, SARs must usually be handled within one month and are generally free of charge. SARs do not always arrive labeled as such, which is why it matters that everyone can spot one:
Customer: Can you send me everything you have on file about me?
Support agent: I'll pass this to our privacy team right away so they can handle it properly.
That second line is the right instinct. Handle the request through the correct escalation process, escalate it promptly, and make sure the relevant teams can locate the data and provide it in the correct format.
Watch out: Never try to handle a subject access request informally on your own. The one-month clock starts when the request is received, not when it reaches the right team.
When something goes wrong
Everyone has a role in keeping data secure, and incidents are usually mundane. Losing a file or device that contains personal data, sending personal data to the wrong recipient, or exposing it through a technical failure all count. Any actual or suspected data loss, theft, unauthorized access, or unauthorized disclosure should be reported to Information Security as soon as it is identified.
Speed matters because the deadlines are short. Under GDPR and UK GDPR, serious personal data breaches must be reported to the relevant supervisory authority, such as the ICO in the UK, within 72 hours of becoming aware of the breach. Where a breach is likely to result in a high risk to the rights and freedoms of individuals, those individuals must also be informed without undue delay. In the US, breach notification obligations vary by state and sector. Prompt internal reporting is what lets the organization contain the incident, assess the risk, and meet those deadlines.
Wrapping up
Privacy starts with knowing what counts as personal data and taking extra care with special category and children's data. Rules differ across the EU, the UK, and the US, so apply the highest appropriate standard where you can. From there it is a set of controls along the lifecycle: design privacy in from the start, be transparent, keep an accurate record, share only with safeguards, and delete data when it is no longer needed. Respect individual rights, escalate subject access requests immediately, and report incidents without delay. Done consistently, these habits protect individuals, support compliance, and build trust.